TL;DR
On May 24th 2022, the Hackerdao (Hackerdao) token was exploited by flashloan attacks, causing a loss of around 200 BNB, which was approximately ~$65,000 at the time of the incident. The stolen BNB was transferred to Tornado Cash immediately afterward.
Summary
At approximately 6:43:50 AM UTC on May 24th 2022, address 0xcfc591 attacked token contract Hackerdao (Hackerdao) via flashloan. There is still not much is known about the Hackerdao project as we write this months later, since the social channels were and are still unknown at time of writing. Despite no social channels, the project has managed to accrue an impressive 38,127 holders. This could potentially be a sign of bot activity on the contract. The project activity on-chain has ceased in the past month, likely due to the long slow death of the project post attack.
The attacker made use of the extra fee charge mechanism of the Hackerdao token contract and the skim mechanism of the pairing pools to manipulate multiple Hackerdao token related pools and drained funds from the pools. As a result the Hackerdao attacker gained approximately ~200BNB worth roughly $65,000 USD at the time of the attack. The incident is a valuable lesson to look back on as the attack vector is unique and could have been avoided with contract auditing.
Attack Flow
The following attack flow is based on the transaction: https://bscscan.com/tx/0x04673c95054247588bb8380dbc7d361f08f8f0baa319366f48ad46e51d08422d (opens in a new tab).
- Flashloan 2,500 WBNB provided by DODO.
- Swap 1,995 WBNB for 10,315 Hackerdao. The Hackerdao - WBNB pool has 1,020 Hackerdao after the swap.
- Transfer 9,007 Hackerdao to the Hackerdao - WBNB pool.
- Call the "skim()" method of the Hackerdao - WBNB pool to transfer the previously sent Hackerdao tokens to another (Hackerdao - USDT) pool.
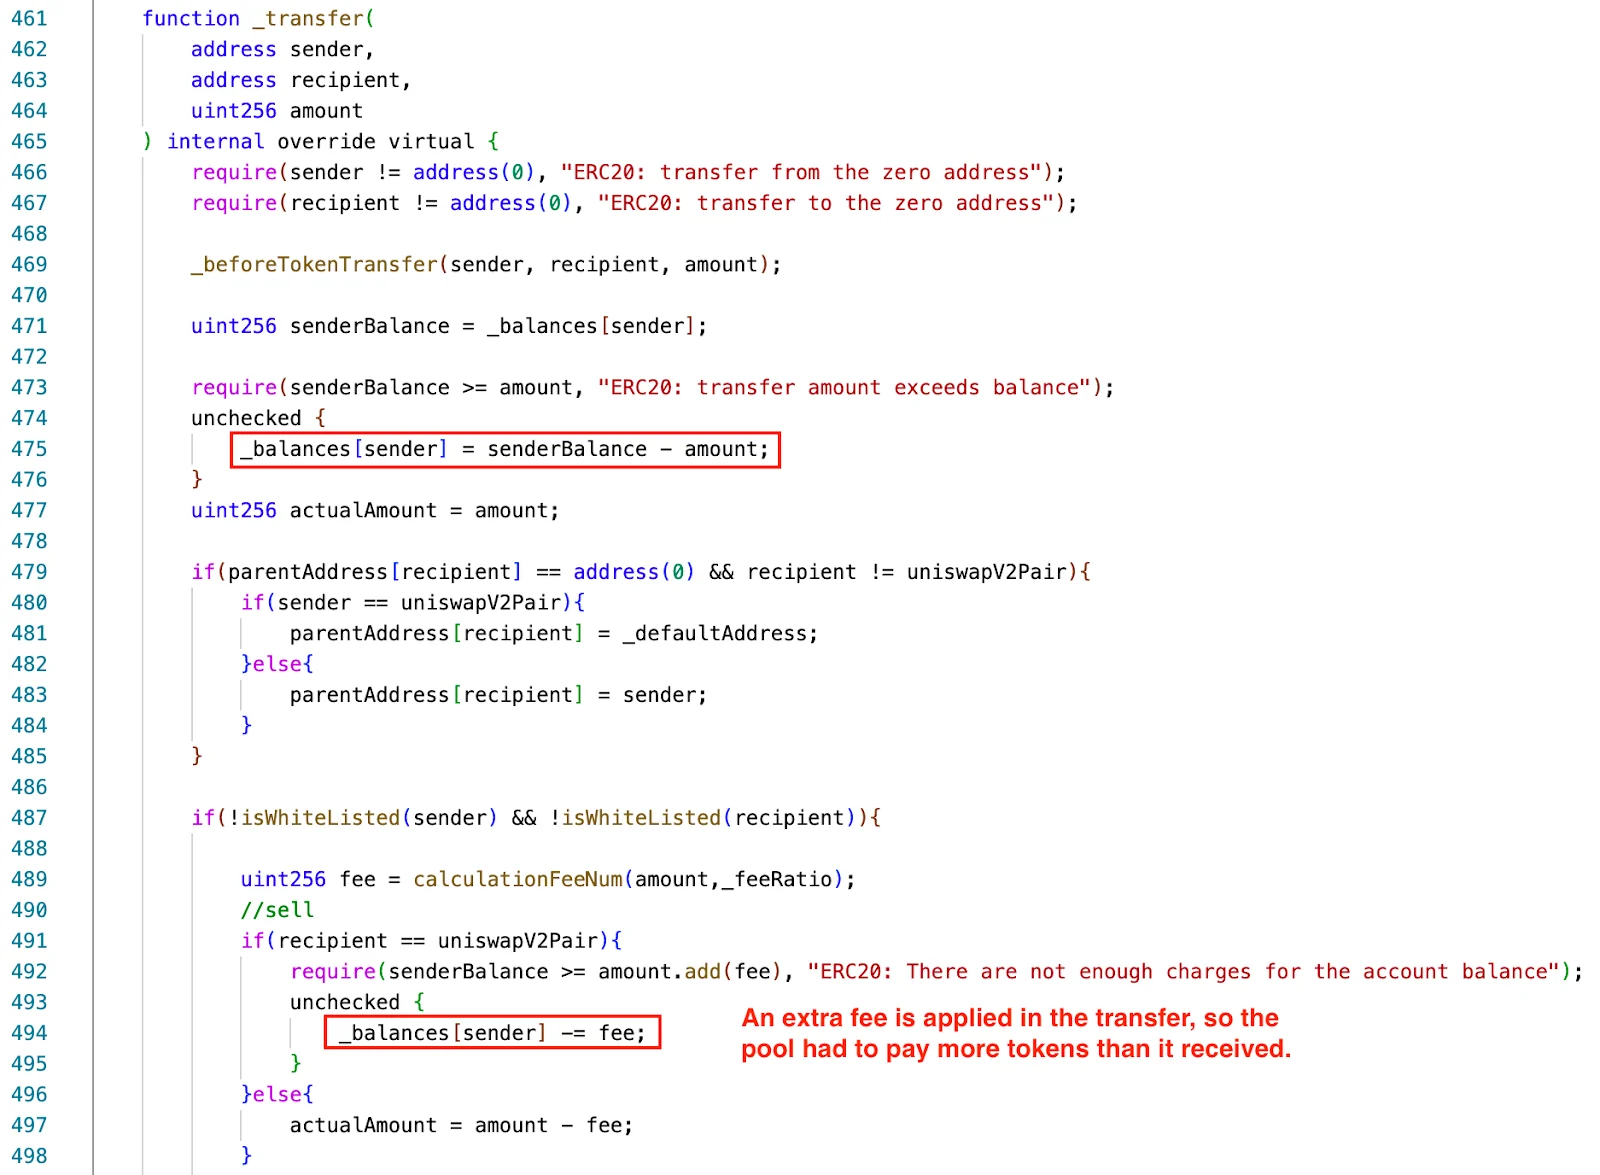
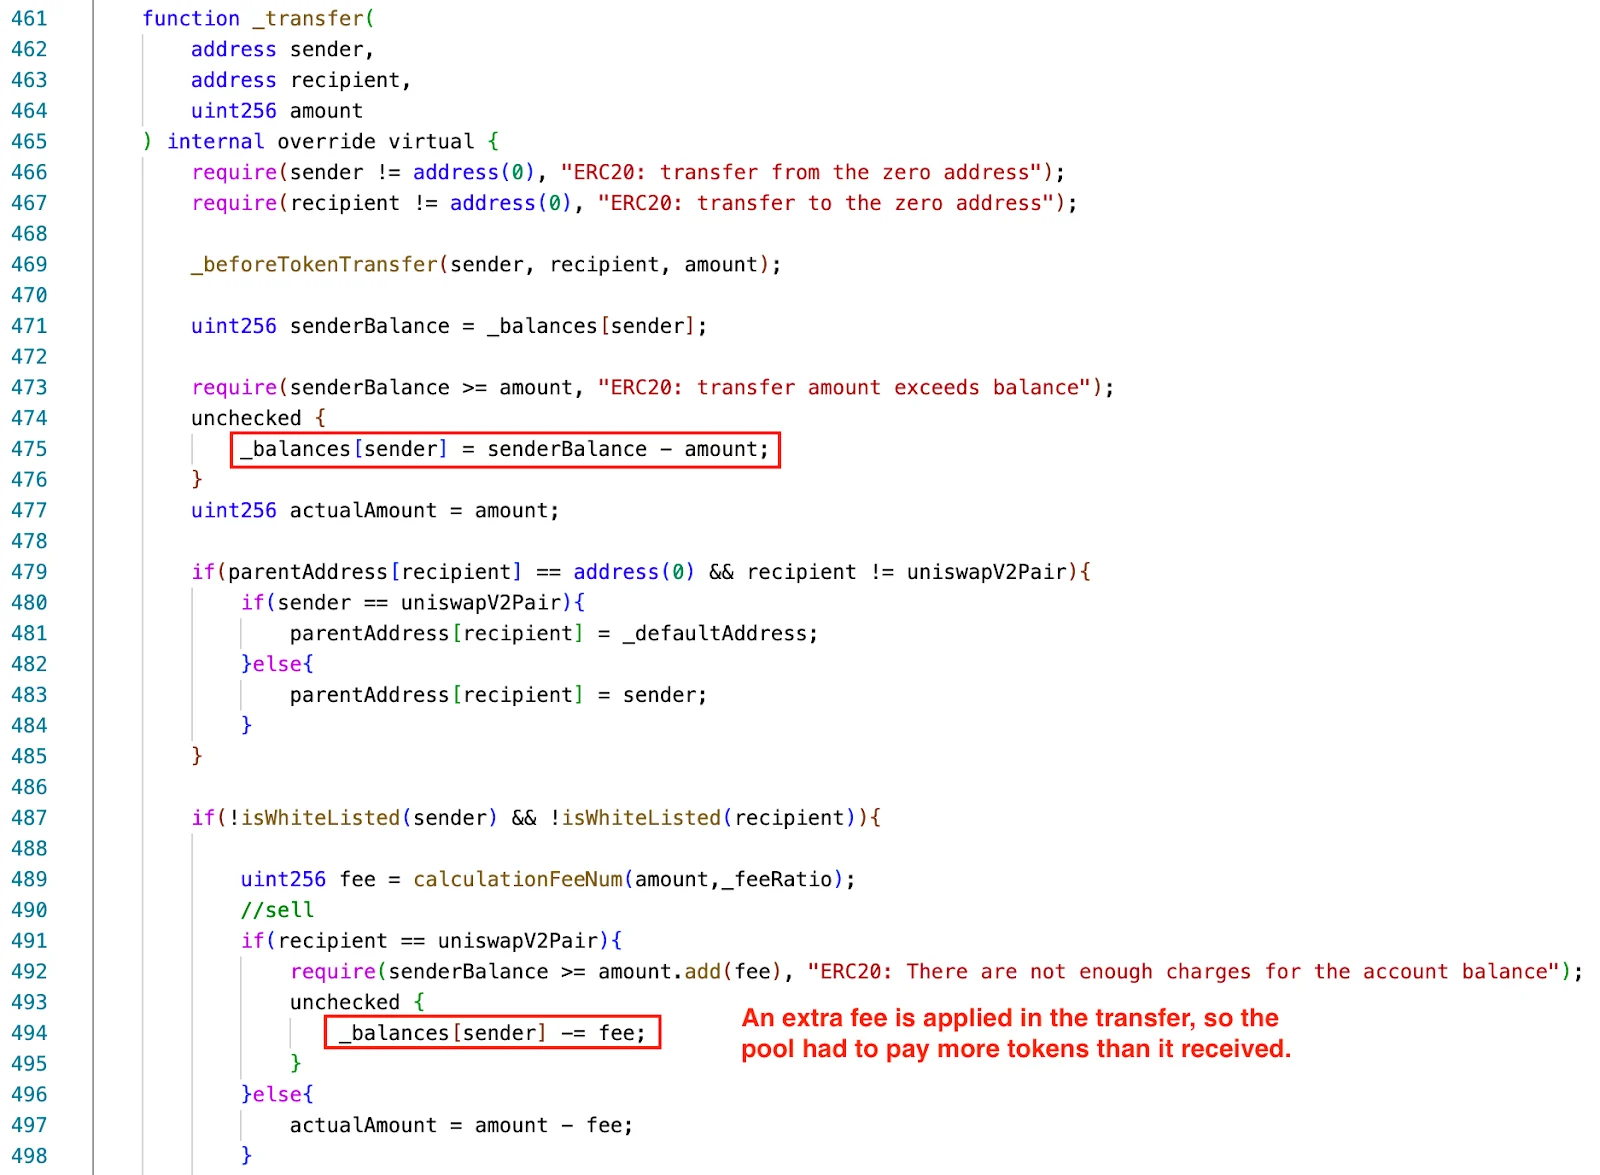
Because Hackerdao charges an extra fee if the recipient is the Hackerdao - USDT pool, the Hackerdao - WBNB pool has to pay more than it received, which led to the result that the Hackerdao - WBNB pool has only 61 Hackerdao after "skim", while the number was 1,020 before "skim".
- Call the "skim()" method of the Hackerdao - USDT pool to get previously sent Hackerdao tokens back.
- Update the price of Hackerdao (reserves) in the Hackerdao - WBNB pool. Because the attacker successfully lower the balance of Hackerdao in the Hackerdao - WBNB pool, the price of Hackerdao was significantly increased.
- Swap 7,029 Hackerdao for 2,170 WBNB. Because the price of Hackerdao was raised, the attacker received more WBNB than he/she paid in Step 2.
- Swap rest of the Hackerdao tokens for USDT and then for WBNB.
- Repay flashloan and receive profits (175 BNB in the first exploit and 24 BNB in the second one).
Contracts Vulnerability Analysis
In the Hackerdao token contract, there is a special logic when recipient is the Hackerdao - USDT pool. The contract will charge an extra fee in the transfer process. Attackers can make use of the functionality and the skim mechanism of UniswapV2Pair contract to drain funds from other pools.
Relevant addresses
Attacker address: https://bscscan.com/address/0xcfc591db031b760961fe8943a183741ed7cd1f82 (opens in a new tab)
Attacker contracts: https://bscscan.com/address/0x24cb6980995aeb7d5a9204e04b17dcd1e99a4694 (opens in a new tab) https://bscscan.com/address/0xafb20f668f37e832512ca91cab1dd9638f42b506 (opens in a new tab)
Hackerdao token contract: https://bscscan.com/address/0x94e06c77b02ade8341489ab9a23451f68c13ec1c (opens in a new tab)
Attacked pool (Hackerdao - WBNB pool): https://bscscan.com/address/0xcd4cdaa8e96ad88d82eabddae6b9857c010f4ef2 (opens in a new tab)
Exploit Transactions
Profit and Assets Tracing
The profit is around 200 BNB (around $65K). It was deposited to Tornado Cash.
https://bscscan.com/address/0xcfc591db031b760961fe8943a183741ed7cd1f82 (opens in a new tab)

Conclusion
After completing their malicious flash loan attack and depositing the ~200 BNB into Tornado Cash, the address has shown no signs of life since. Furthermore, the Hackerdao project has seen massive reductions in activity and at time of writing has seen only 5 transactions in the past 30 days. This attack highlights an ongoing problem within the ecosystem of smaller token projects where if there exists a vulnerability it will be exploited and more often than not, destroy momentum of the project. With contract auditing, many of these projects could grow without the growing pains of contract vulnerability. Get audited today!